
Third-Party Risk Management
Control vendor risk. Protect operational continuity. Satisfy regulatory expectations.
Financial institutions increasingly rely on an expansive ecosystem of third parties — cloud providers, software vendors, payment processors, and specialized service partners. While third parties drive scale and operational agility, they also import cyber, operational, regulatory, and concentration risks directly into your enterprise.
Yuwa Solutions designs and operationalizes end-to-end TPRM frameworks calibrated to Canadian regulatory expectations (OSFI B-10, FCAC third-party oversight, FINTRAC, and CIRO). We build practical vendor tiering, rigorous due diligence, continuous monitoring, and exit planning that protect institutional integrity without slowing down procurement.
Our TPRM Capabilities
Explore our core third-party risk management services. Select any practice area below to navigate directly to its methodology, deliverables, and stakeholder coverage.
Vendor Inventory & Risk Tiering
Establish a comprehensive inventory of all third-party engagements and implement a defensible multi-factor tiering model calibrated to Canadian regulatory materiality standards.
Due Diligence Framework Design
Design tiered pre-contract due diligence questionnaires, evaluation scorecards, and cross-functional review workflows tailored to vendor risk profiles.
Inherent & Residual Risk Assessment
Quantify gross exposure from outsourced services, evaluate compensating vendor and internal controls, and establish defensible residual risk ratings.
Contract & SLA Review Support
Embed mandatory risk, security, and continuity provisions into third-party contracts — including audit rights, incident notification windows, and regulatory compliance covenants.
Ongoing Monitoring Programme
Establish risk-based monitoring cadences, trigger-based reassessments, security posture scoring, and annual review cycles for active vendor relationships.
Concentration Risk Analysis
Analyze cross-functional dependency on single providers, shared infrastructure (cloud regions, sub-contractors), and geographic concentrations across your critical operations.
Exit & Contingency Planning
Develop pragmatic exit strategies, transition timelines, and data repatriation protocols for critical outsourced functions to protect business continuity upon termination.
TPRM Tool Implementation Support
Select, configure, and operationalize GRC and specialized TPRM software platforms to streamline assessments, vendor questionnaires, and workflow tracking.
TPRM Governance & Reporting
Establish third-party risk committee charters, escalation thresholds, executive dashboards, and board reporting templates aligned with regulatory expectations.

Classifying vendor risk based on materiality, data sensitivity, and operational impact.
Vendor Inventory & Risk Tiering
What It Is
A defensible TPRM programme begins with knowing every vendor and the risk they represent. Without structured tiering, organisations spend equal effort assessing low-risk commodity suppliers and mission-critical cloud platforms. Yuwa Solutions designs multi-factor vendor tiering models that assess data access, operational criticality, substitute availability, and regulatory materiality to ensure risk oversight effort matches risk exposure.
What We Deliver
Procurement, risk, and compliance leaders seeking a structured, defensible basis for prioritizing third-party risk management resources.

Proportionate, evidence-based vetting before contracts are signed.
Due Diligence Framework Design
What It Is
Pre-contract due diligence is your primary opportunity to identify vendor vulnerabilities before they enter your operational environment. Generic, 300-question questionnaires frustrate vendors and bury critical risks under administrative noise. Yuwa Solutions designs targeted, risk-proportionate due diligence frameworks spanning information security, business continuity, financial viability, regulatory compliance, and fourth-party risk.
What We Deliver
Sourcing teams, information security officers, and risk managers needing consistent, defensible onboarding assessment standards.

Measuring gross exposure and validating mitigating vendor controls.
Inherent & Residual Risk Assessment
What It Is
Effective third-party management separates the inherent risk of the outsourced activity from the residual risk that remains after vendor controls and internal safeguards are applied. Yuwa Solutions builds structured assessment methodologies that evaluate SOC 2 reports, ISO certifications, penetration test summaries, and disaster recovery audits to establish reliable residual risk ratings across your supplier base.
What We Deliver
Enterprise risk managers, IT risk teams, and audit committees requiring defensible metrics on vendor-related exposure.
Enforcing audit rights, notification triggers, and regulatory clauses in vendor agreements.
Contract & SLA Review Support
What It Is
Your contractual terms represent your strongest legal protection when a vendor fails or suffers an incident. Many financial institutions discover gaps in their contracts only after an outage occurs. Yuwa Solutions supports legal and procurement teams by developing standard TPRM contract schedules, SLA requirements, breach notification timelines, and business continuity covenants aligned with OSFI B-10 and FCAC standards.
What We Deliver
General counsel, procurement directors, and contract managers seeking to align third-party agreements with regulatory expectations.

Moving from point-in-time assessments to proactive, continuous vendor oversight.
Ongoing Monitoring Programme
What It Is
Vendor risk changes throughout the contract lifecycle. A vendor that passed onboarding due diligence can suffer security degradation, leadership turnover, or financial distress. Yuwa Solutions designs ongoing monitoring programmes that combine periodic recertification, external threat intelligence monitoring, SLA performance reviews, and trigger-based assessments following major organizational or operational changes.
What We Deliver
Vendor relationship managers, operational risk officers, and CISO teams managing multi-year third-party relationships.

Uncovering single vendor dependencies and geographic concentration across business units.
Concentration Risk Analysis
What It Is
Concentration risk occurs when multiple critical business functions rely on the same third party, or when different suppliers all depend on the same underlying cloud infrastructure or geographic hub. Regulators increasingly demand that financial institutions demonstrate visibility into concentration risk. Yuwa Solutions maps enterprise-wide spend, operational dependency, and fourth-party concentrations to identify and mitigate systemic failure points.
What We Deliver
Enterprise risk leaders, operational resilience heads, and technology architects addressing systemic external dependencies.

Actionable transition strategies and data return protocols when vendor contracts terminate.
Exit & Contingency Planning
What It Is
Regulators require institutions to have documented exit plans for critical outsourcing arrangements. An exit plan outlines how the institution would transition a critical service to an alternative provider or bring it back in-house in the event of vendor insolvency, material breach, or strategic termination. Yuwa Solutions creates actionable exit playbooks specifying data migration, transition windows, and interim workarounds.
What We Deliver
Business continuity managers, Chief Information Officers, and business unit leaders responsible for critical outsourcing contracts.
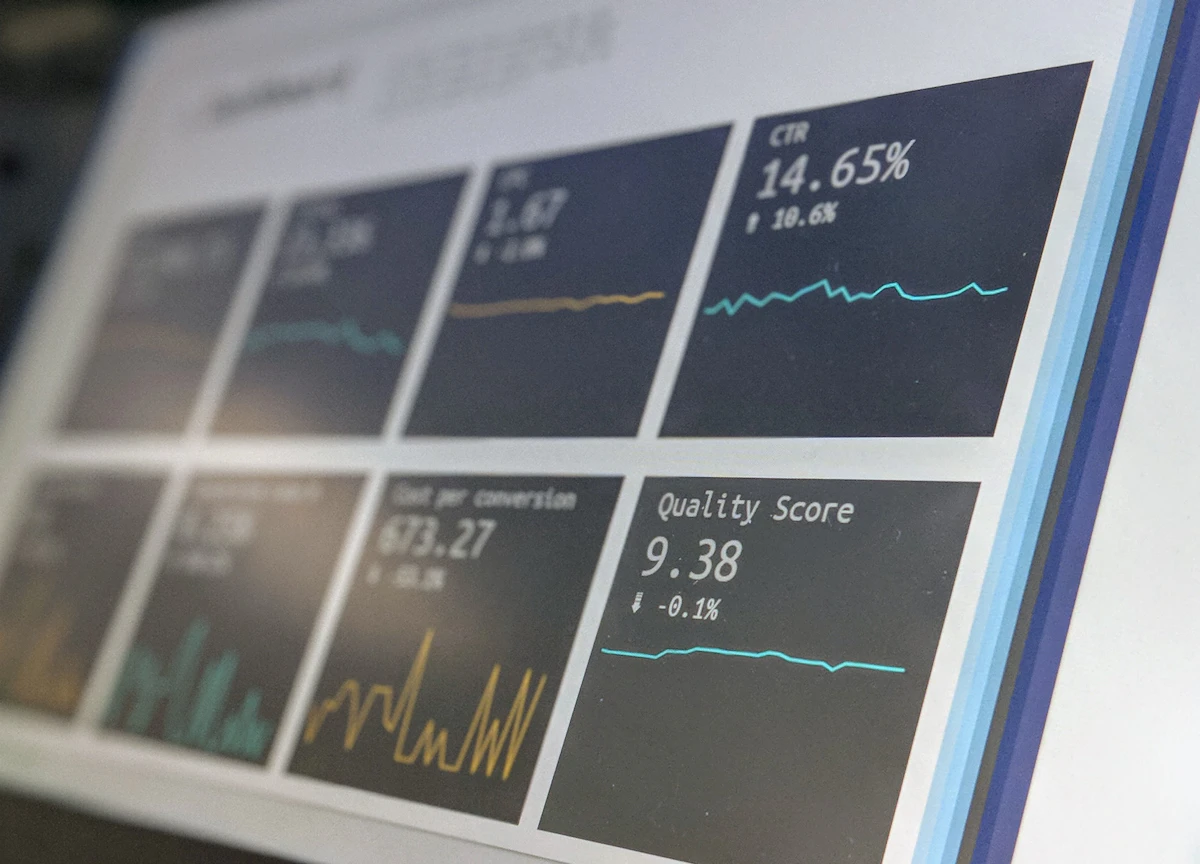
Configuring GRC and TPRM platforms to match your operating model, not vendor defaults.
TPRM Tool Implementation Support
What It Is
Spreadsheet-based TPRM programs break down once an institution manages more than fifty vendors. Specialized TPRM tools automate questionnaire delivery, security rating feeds, and renewal tracking — but only if configured around a sound methodology. Yuwa Solutions provides vendor-neutral tool selection advisory, workflow design, and configuration support to ensure your technology platform delivers measurable operational efficiency.
What We Deliver
Organizations transitioning from manual spreadsheets to enterprise TPRM/GRC software platforms.

Board-ready oversight, committee charters, and third-party risk appetite metrics.
TPRM Governance & Reporting
What It Is
Boards and senior executives must maintain ultimate oversight of third-party arrangements. TPRM governance establishes who has the authority to approve high-risk vendors, when exceptions may be granted, and how vendor risk exposure is communicated to leadership. Yuwa Solutions builds governance frameworks that give executives clear visibility and defensible control over their external supplier ecosystem.
What We Deliver
Chief Risk Officers, General Counsel, and Board Risk Committees seeking rigorous oversight of outsourced operations.
Our Approach to Third-Party Risk
Third-party risk management is not a one-time onboarding checklist. It is a lifecycle governance discipline. We design programmes that balance regulatory compliance with commercial pragmatism — ensuring critical vendors are rigorously governed without paralyzing business operations.
Proportionate to Materiality
We eliminate assessment fatigue by focusing rigorous evaluation on the minority of suppliers that truly impact operational continuity, customer data, and regulatory compliance.
Evidence-Based Verification
We look beyond vendor self-attestations to validate independent audit reports, security telemetry, continuity test evidence, and contractual commitments.
Full Lifecycle Governance
Third-party risk management is an ongoing lifecycle — from sourcing and contracting to continuous monitoring and structured exit — not a one-time onboarding checkpoint.
Regulatory Alignment by Design
Our frameworks are directly mapped to Canadian regulatory expectations (OSFI B-10, FCAC third-party oversight, FINTRAC, CIRO), ensuring defensibility during regulatory examinations.
Frequently Asked Questions
Practical answers to common questions about vendor tiering, OSFI B-10 compliance, concentration risk, and exit planning.
Ready to strengthen your third-party risk framework?
Speak directly with our third-party risk specialists to assess your vendor tiering, concentration exposure, and regulatory compliance readiness.